
- Ledger confirmed a hidden implant that stole recovery phrases during wallet setup.
- The spy chip transmitted stolen recovery words over a mobile connection.
- Bitquery estimates $102 million was stolen across 324 wallets.
In early October, customers in Southeast Asia discovered that their crypto had disappeared from Ledger hardware wallets that still seemed to be working normally.
They bought the devices through CryptoBilis, an authorized reseller, and believed their private keys were protected inside a device built for that purpose. What they couldn’t see was a second piece of hardware, hidden inside the casing, that could steal the information needed to empty the wallet.
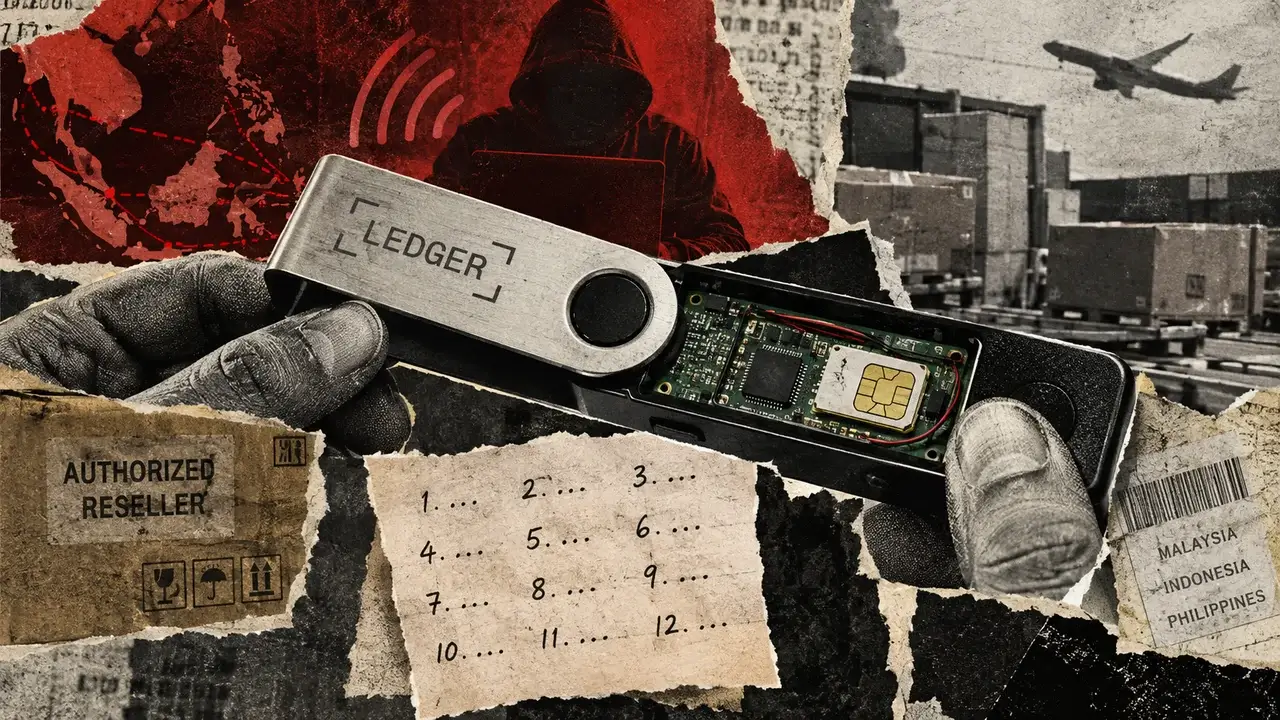
On Oct. 10, Ledger confirmed an unauthorized implant in one affected customer’s device. Three days later, its security team explained that the added electronics had read the wallet’s 24 recovery words as they appeared on the screen during setup and sent them over a mobile connection.
The protected chip, operating system, and transaction signatures were unchanged.
Blockchain analytics firm Bitquery estimates that attackers stole $102 million from 324 wallets across six networks, although Ledger hasn’t confirmed that total or established that every loss came from an implanted device.
The moment the secret leaves the chip
Hardware wallets don’t actually hold crypto. The coins remain on their networks, so the device only protects the private keys used to authorize transactions, keeping those secrets away from malware on an internet-connected phone or computer.
When an owner approves a payment, the wallet signs the transaction without giving the computer those keys. That separation is the product’s main promise, but one exception appears before every owner makes a first payment.
During setup, a Ledger wallet displays 24 recovery words, which can recreate the wallet and its keys if the device is lost. Owners are told to write the phrase down, keep it offline, and never share it. Anyone who copies it can restore the same accounts on another device, and the original wallet’s PIN will not stop them.
The CryptoBilis implant was designed for that brief moment when the words appeared on the screen. According to Ledger, a small controller intercepted the information being sent to the display, reconstructed the phrase, and transmitted it over LTE using an embedded SIM card.
It didn’t need to break the protected chip or trick the owner into entering the words on a fake website.
The owner could finish setup, use the wallet, and approve legitimate transactions, while someone else had an identical way to access the funds. An optional additional passphrase can protect accounts created with it, but for ordinary accounts the recovery words alone are enough.
A real check with a real blind spot
Ledger’s Genuine Check verifies that a device contains an authentic Secure Element, the chip responsible for sensitive security operations. It can identify a counterfeit chip, but it can’t inspect every component inside the casing or prove that nothing has been added since manufacture.
Ledger’s security documentation warns that physical modifications may escape detection when the original chip remains intact. That’s the weakness the implant exploited: the device could truthfully report on its Secure Element while failing to reveal the extra circuitry beside it.
Tibane Labs examined modified Ledger Nano X devices fitted with electronics that monitored signals between the secure chip and the screen. A more sophisticated specimen used a custom board hidden beneath the display and kept the device’s original battery, so casual inspection couldn’t find it.
Those specimens were separate from the CryptoBilis investigation and don’t prove that the same devices or attackers were involved. They do, however, explain why an authentic chip, correct signatures, and a normal-looking wallet are not the same as proof that the entire device is untampered.
Ledger wallet implant exposes a gap in its authenticity check
The weak point was the journey to the buyer
CryptoBilis was an authorized reseller operating in Malaysia, Indonesia, and the Philippines. Customers weren’t taking a reckless shortcut by buying there, as Ledger itself recommends buying through authorized sellers.
That’s what makes the case more consequential than a counterfeit wallet bought from an anonymous seller. The question was whether the product could be trusted after passing through distributors, retailers, and anyone else with access to the stock.
In an Oct. 15 update, Ledger said attackers bought genuine devices over several months, opened them, fitted custom components, and returned them to distribution through Southeast Asian resellers.
The company described the incident as an attack on the distribution channel and said samples checked in warehouses and stores showed no tampering.
Ledger also said it had asked authorized resellers and distributors in Southeast Asia and Hong Kong to suspend sales. It’s tightening controls on returned products and asking sellers to keep devices off display shelves, measures that acknowledge how important physical access becomes when attackers can modify a product without changing the software inside it.
Germany’s MediaMarktSaturn suspended Ledger sales following a report of a tampered device, while rival wallet maker Trezor moved to reduce its reseller network despite finding no evidence that its own products were compromised.
Bitquery found that 25 Tron wallets signed the same approval within three seconds, a pattern consistent with someone already controlling multiple accounts.
But blockchain records can’t identify who opened a package, installed a component, or returned a device to a shop. That requires hardware examinations and distribution records.
A new device is not enough
For anyone who may have received a compromised wallet, the important difference is between the device and the recovery phrase. A PIN protects the original device from unauthorized use, but it does nothing to stop someone from restoring the same keys elsewhere.
Buying new hardware and entering the old 24 words recreates the same risk. The assets need to move to accounts generated from a fresh recovery phrase on a trusted device, using carefully verified addresses and instructions.
Ledger has told people who bought from CryptoBilis not to initialize unused devices and advised those who already set them up to move funds to a new signer with a new phrase. Affected owners should use official support channels, preserve potentially relevant evidence, and never provide recovery words to someone claiming they can help recover the money.
The incident shows that the security boundary people think they are buying extends beyond the chip inside the device. It extends through the screen, casing, packaging, and distribution chain, all the way to the moment the recovery words first appear.
Self-custody removes the need to trust an exchange to hold the keys, but not the need to trust the hardware that creates and displays them. In the CryptoBilis case, the attackers didn’t have to wait for an owner to make a mistake after opening the box, because they gained access long before the owner even arrived.
Related CompanyTrezorHardware wallet manufacturerRelated CompanyLedgerCrypto hardware wallets
AnalysisHacksCrimeWallets
